 Enlarge documentation
FILE INJECTION
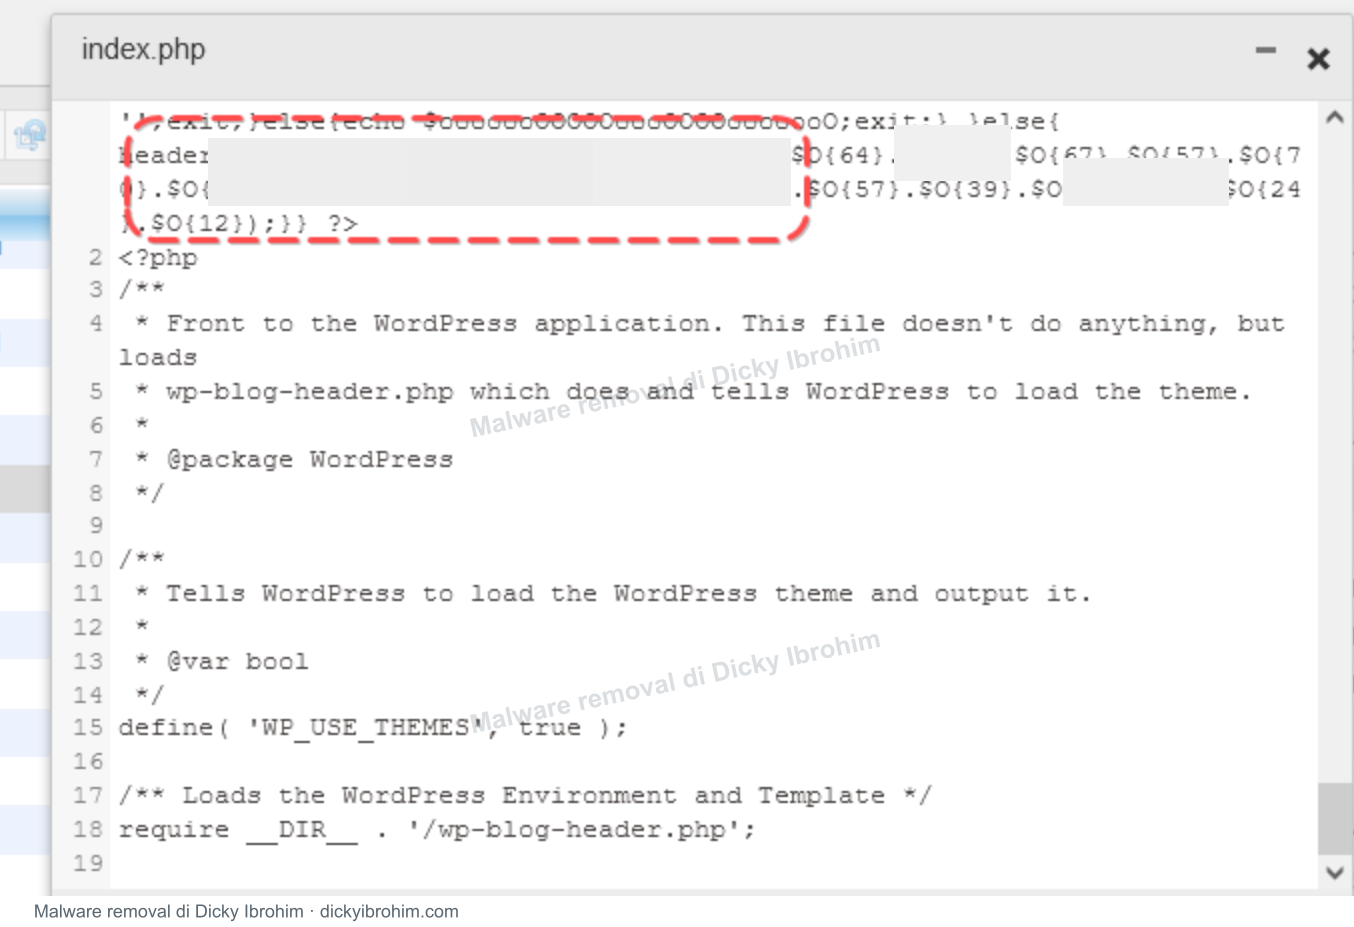
An insertion before the application code.
Unfamiliar code appears before WordPress loads. Sensitive details are covered; website functionality still needs testing after cleanup.
MALWARE REMOVAL · WORK DIRECTLY WITH ME
JAKARTA, INDONESIA · REMOTEVisitors sent elsewhere, unfamiliar ads, or an advertising rejection linked to your website? I help remove malware from custom websites and WordPress, investigate what caused the problem, and retest the affected functionality.
 Work directly with me, Dicky Ibrohim. Start with what you have noticed.
Record symptoms and back up files and the database before making changes, wherever access allows.
Inspect folders, core files, plugins, and suspicious changes. Review findings before taking action.
Quarantine findings for review, remove confirmed injections, and restore files from trusted sources.
Inspect settings, content, and accounts for injections. Clean affected records while preserving legitimate data.
Adjust permissions, review accounts and sessions, and update vulnerable components for the website’s needs.
Check file integrity, redirects, and functions on desktop and mobile. Document the results and next steps.
Illustrated remediation workflow
SELECTED DOCUMENTATION
These excerpts show types of disruption and one notification following remediation. Each website needs its own assessment; a result from one engagement is not a promise for another.
Identities, addresses and brand names are redacted. Some views have been reconstructed for readability. Several images show details from the same documentation.
Enlarge documentation FILE INJECTION
Unfamiliar code appears before WordPress loads. Sensitive details are covered; website functionality still needs testing after cleanup.
 Enlarge documentation
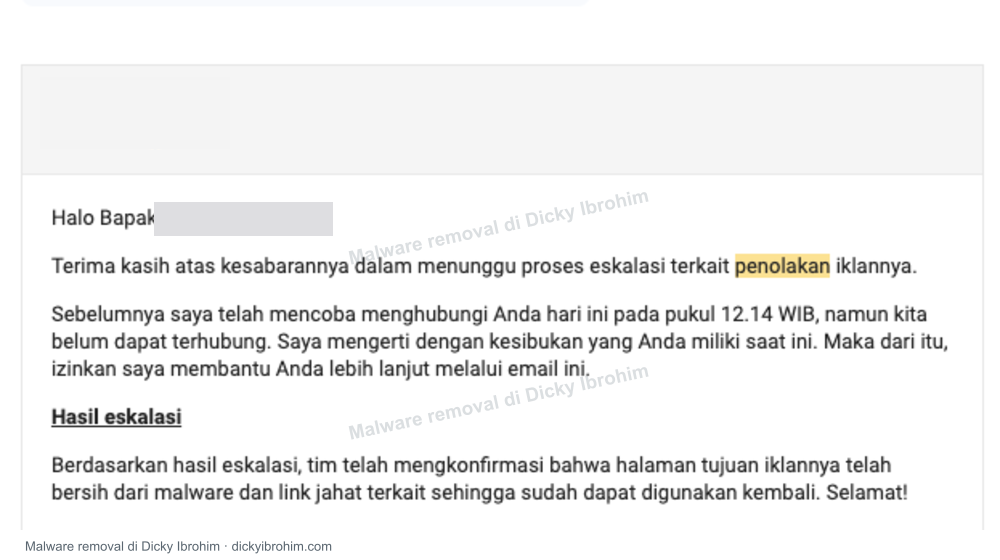
DESTINATION REVIEW
An excerpt of a notification stating that the destination could be used again following review. It records that outcome, without guaranteeing advertising approval or implying affiliation with the provider.
 Enlarge documentation
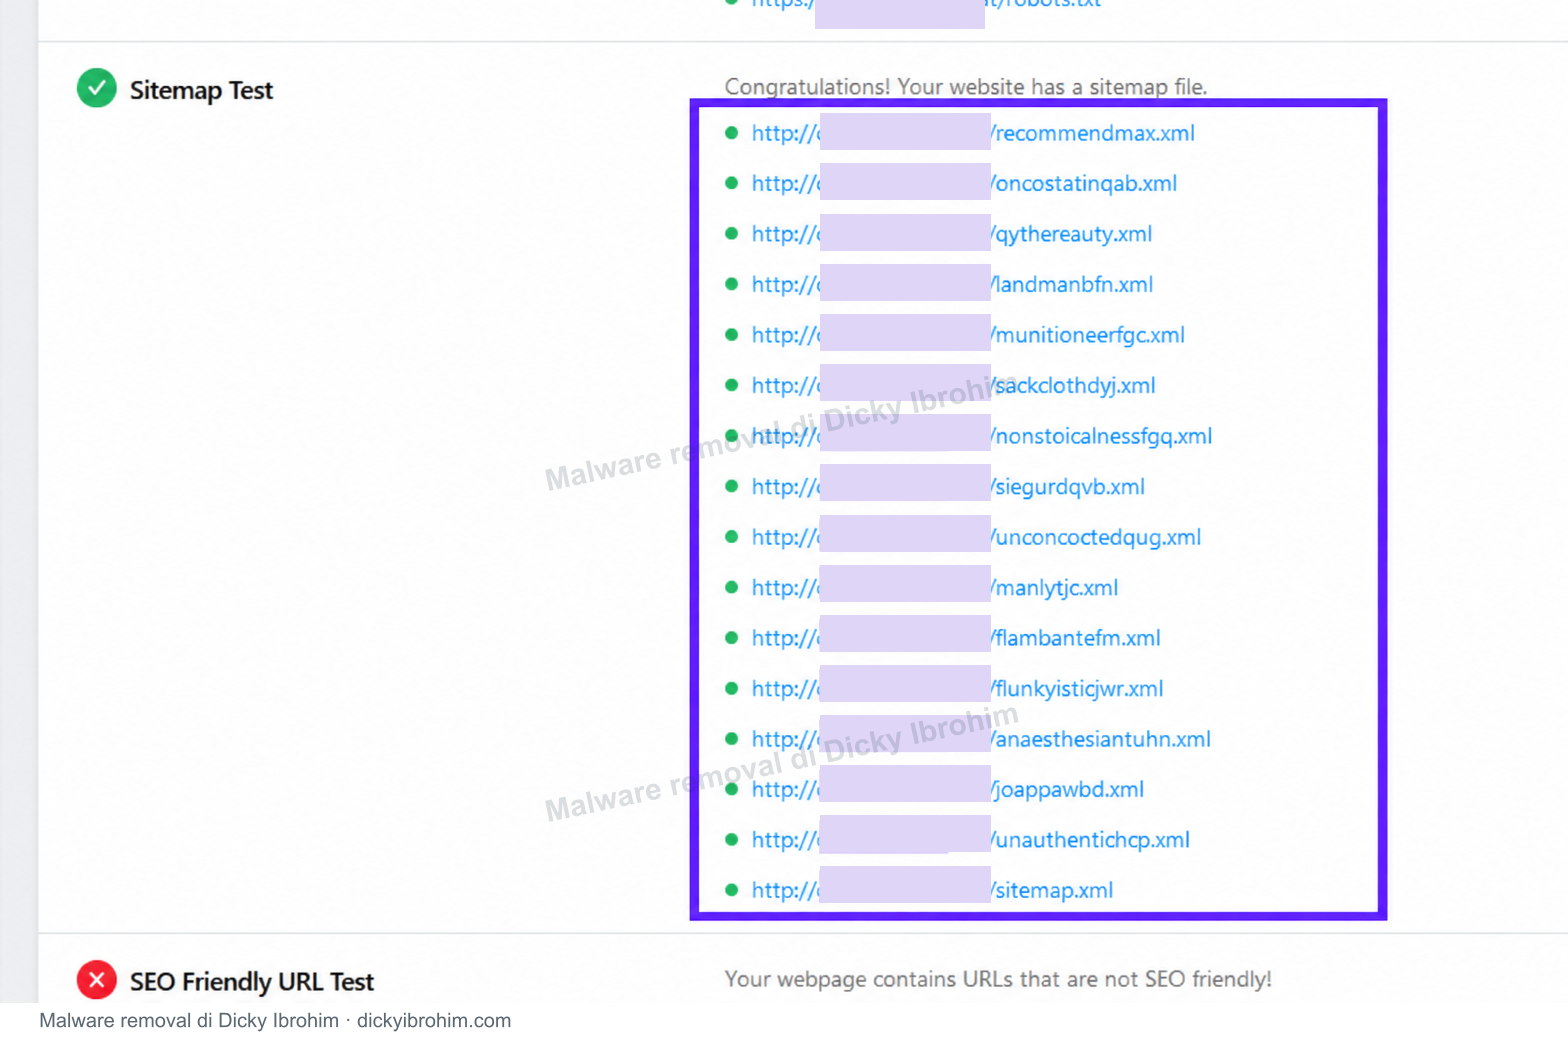
SITEMAP SPAM
Unfamiliar sitemaps provide a starting point for tracing injected content and whatever generates it.
 Enlarge documentation
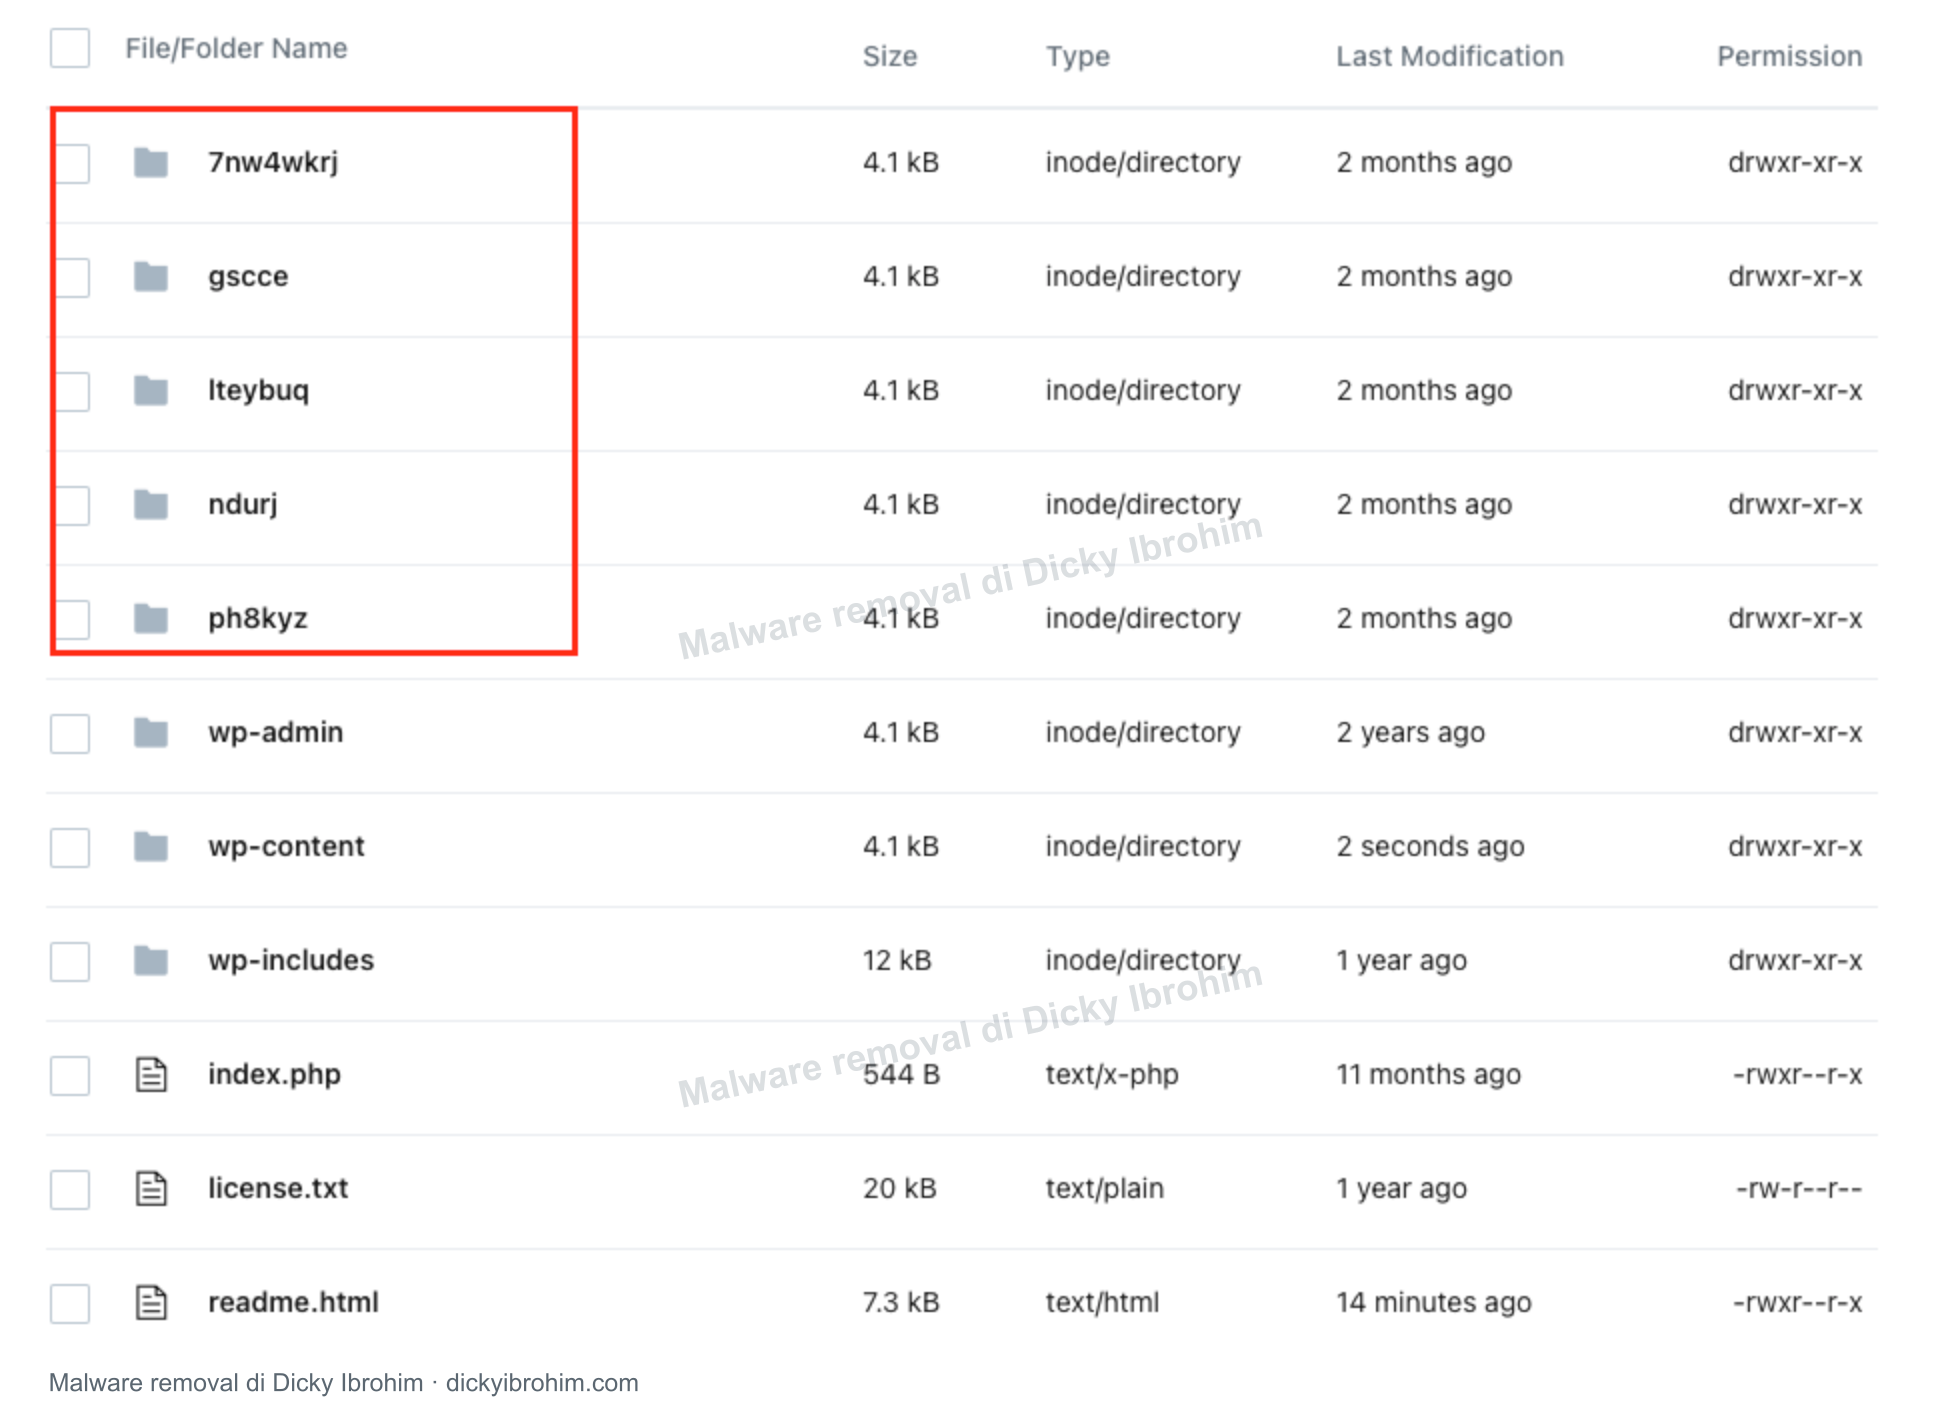
UNFAMILIAR DIRECTORIES
A directory list from documentation of injected advertising on mobile. Folder names alone do not establish their function; contents and behavior need investigation.
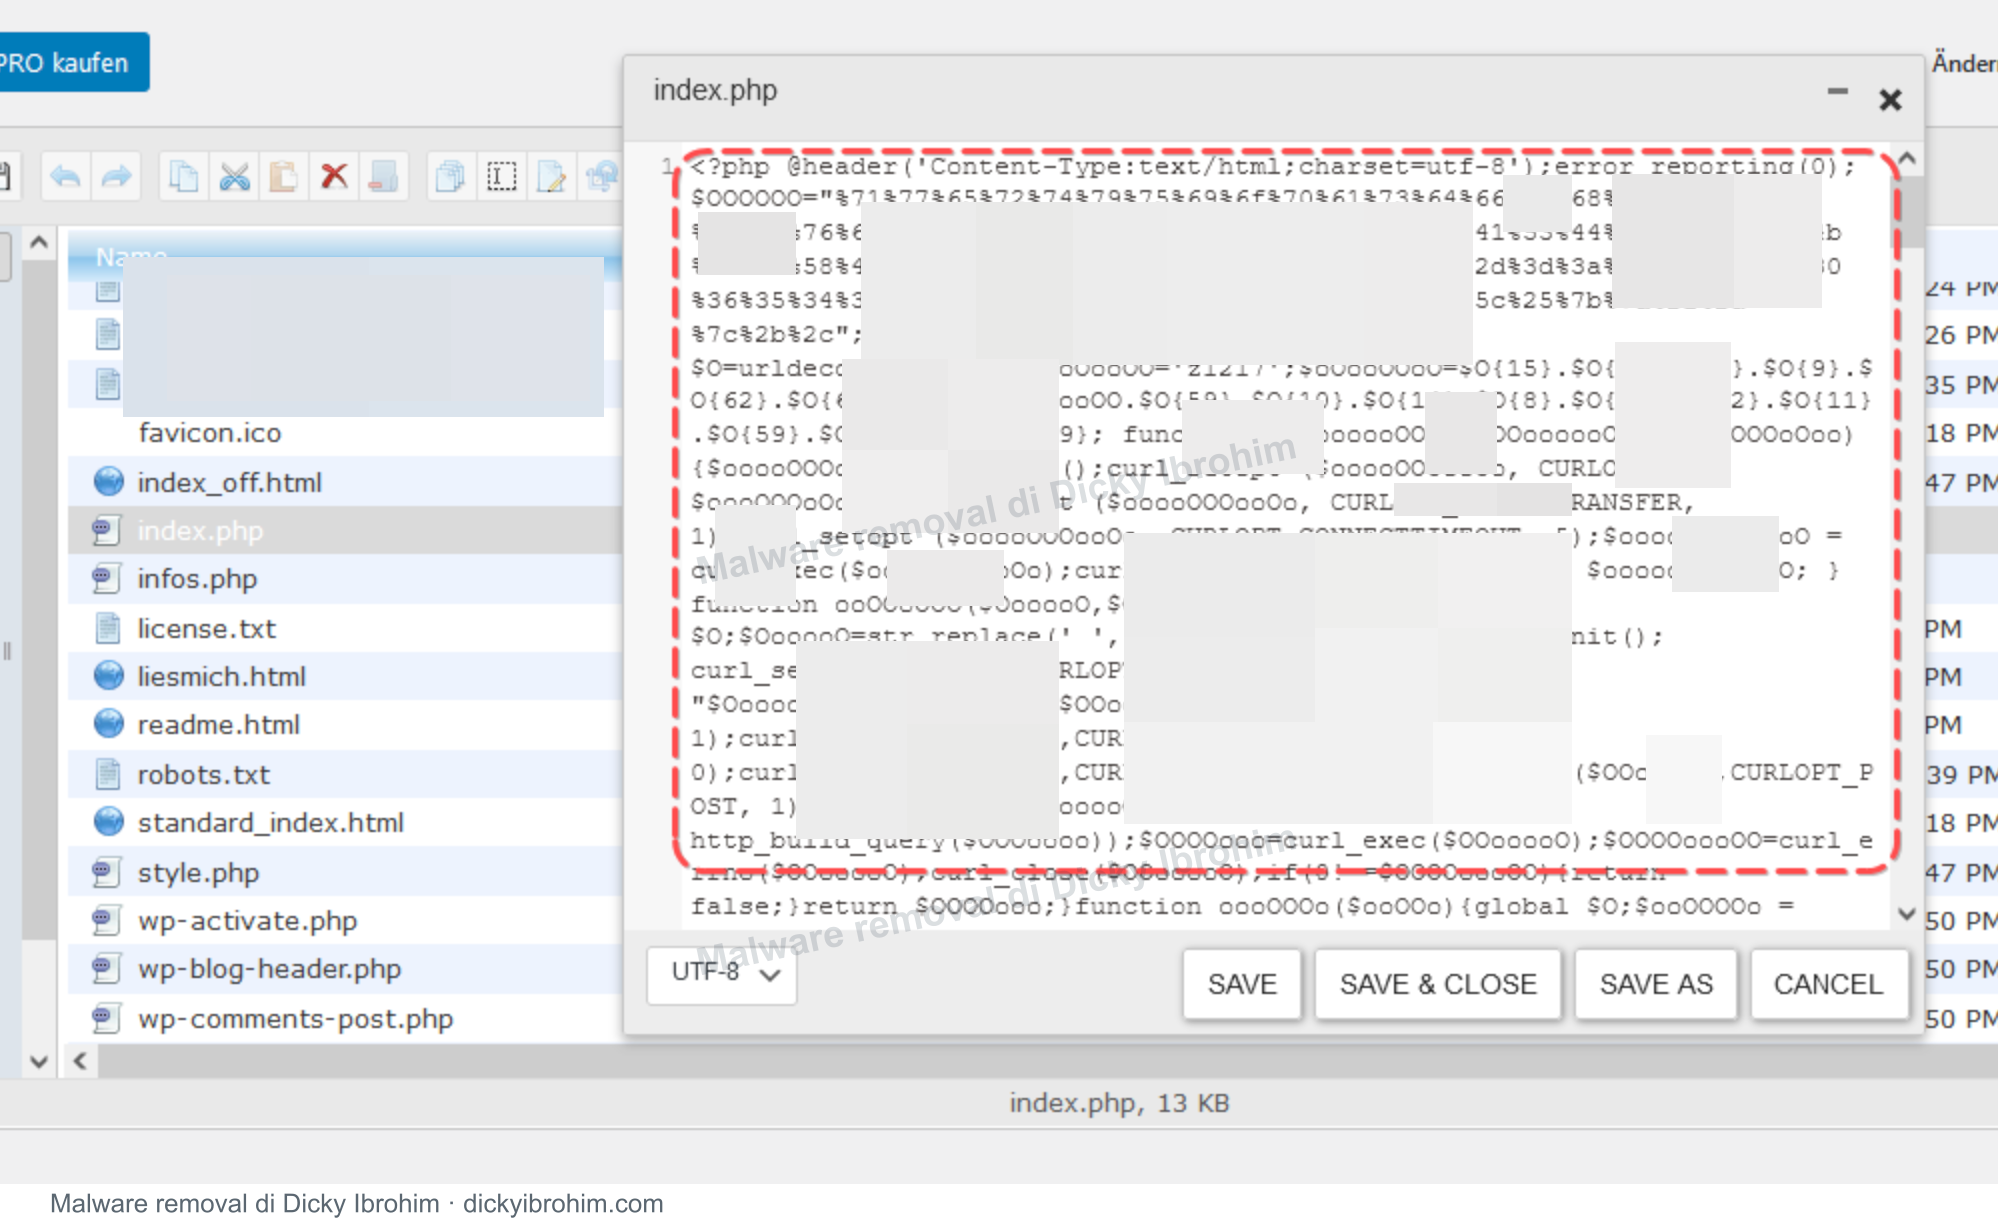 Enlarge documentation
FILE INSPECTION DETAIL
Obfuscated code in the entry file marks an area for analysis. Sensitive content is covered in this public copy.
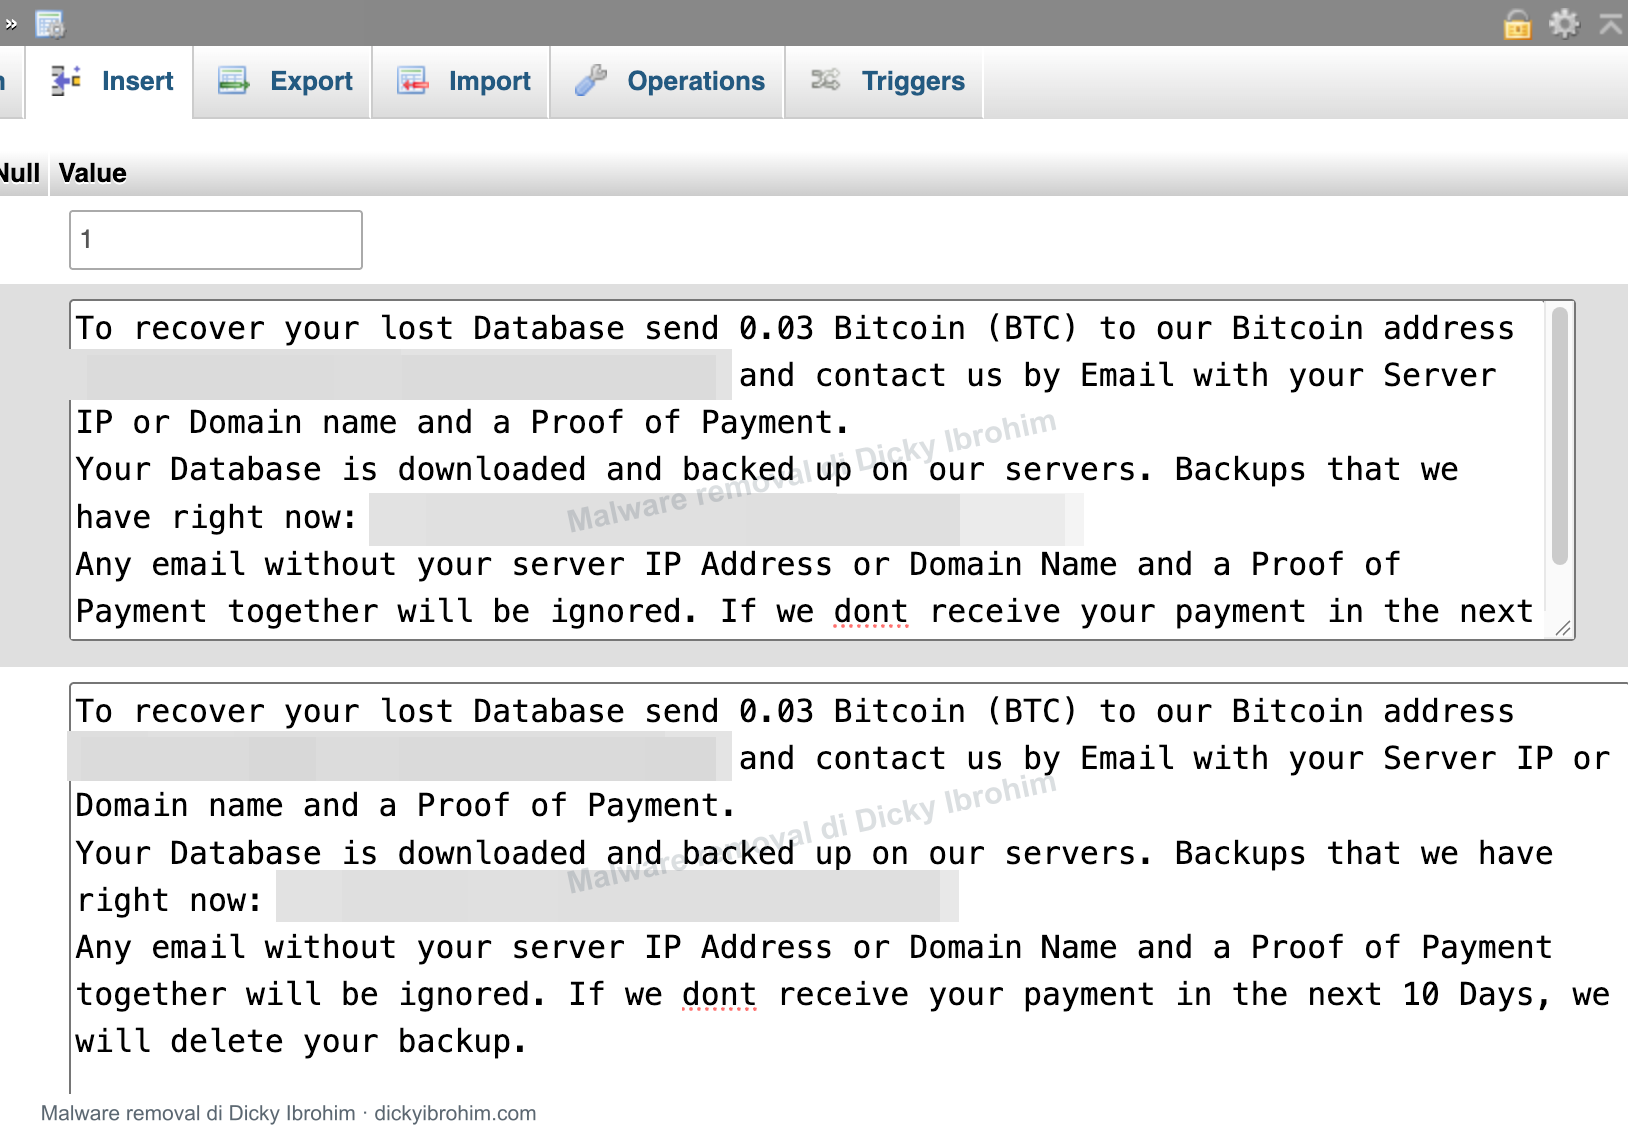 Enlarge documentation
DATABASE INCIDENT
Documentation of a threatening message. Backup availability and data integrity need separate checks before assessing recovery options.
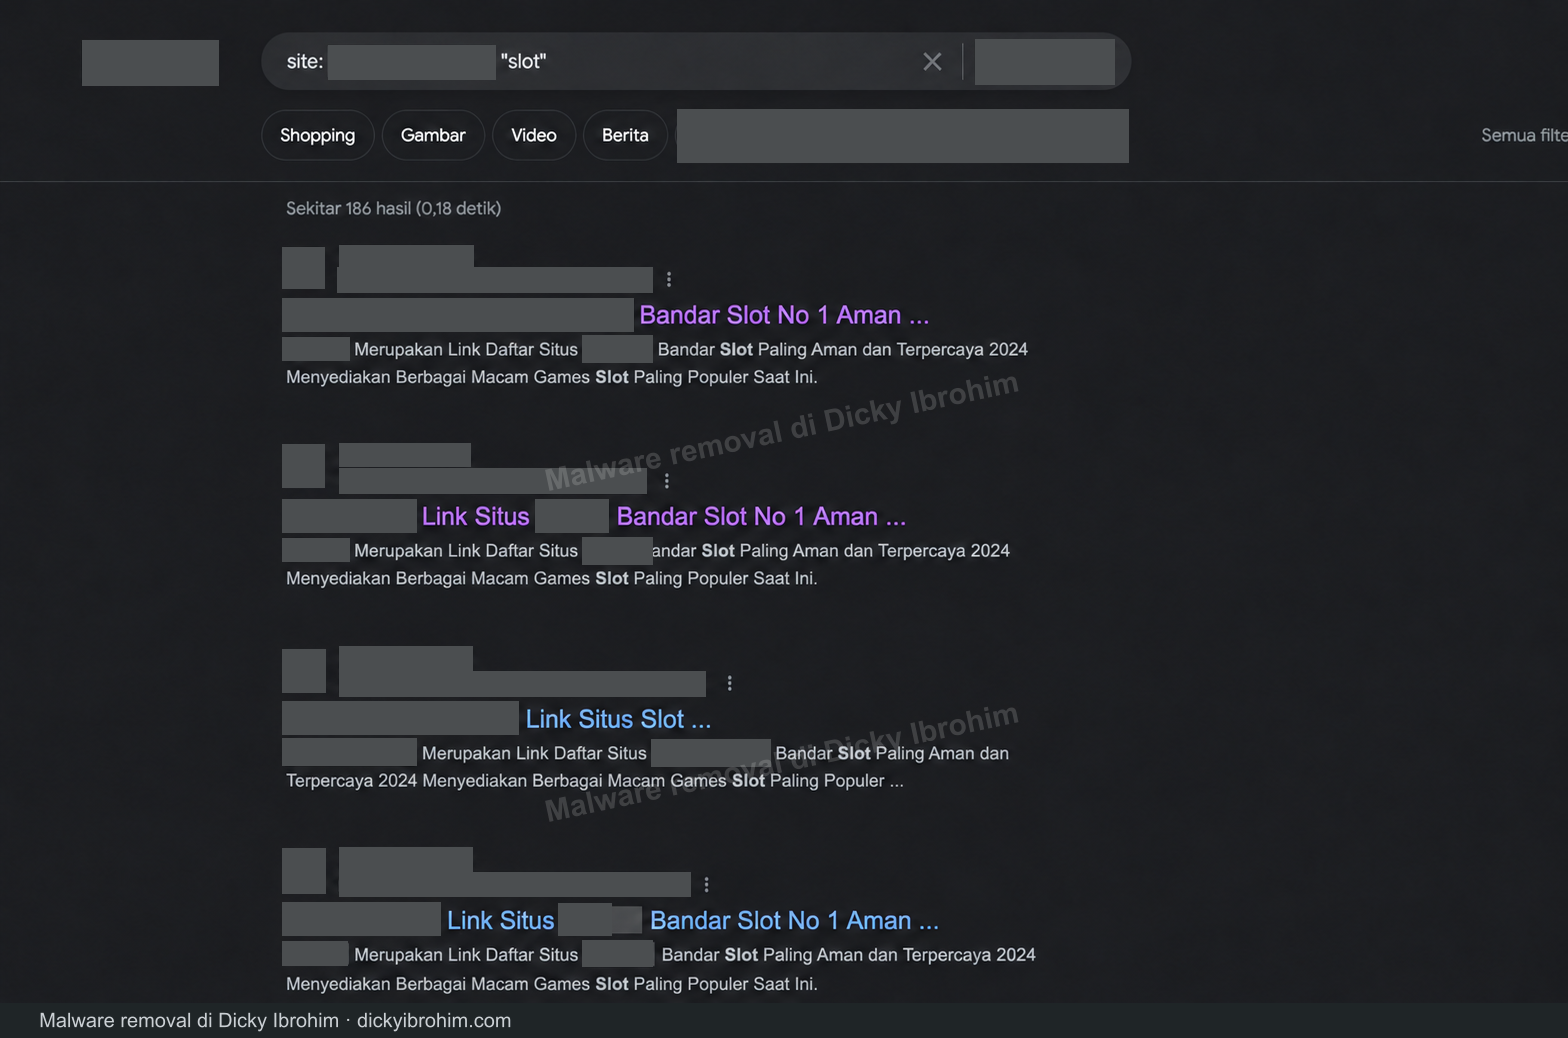 Enlarge documentation
SEARCH SPAM
A search view affected by unauthorized content. Domains and brand names are redacted, while result excerpts remain visible to show the disruption. This documents spam and does not promote it.
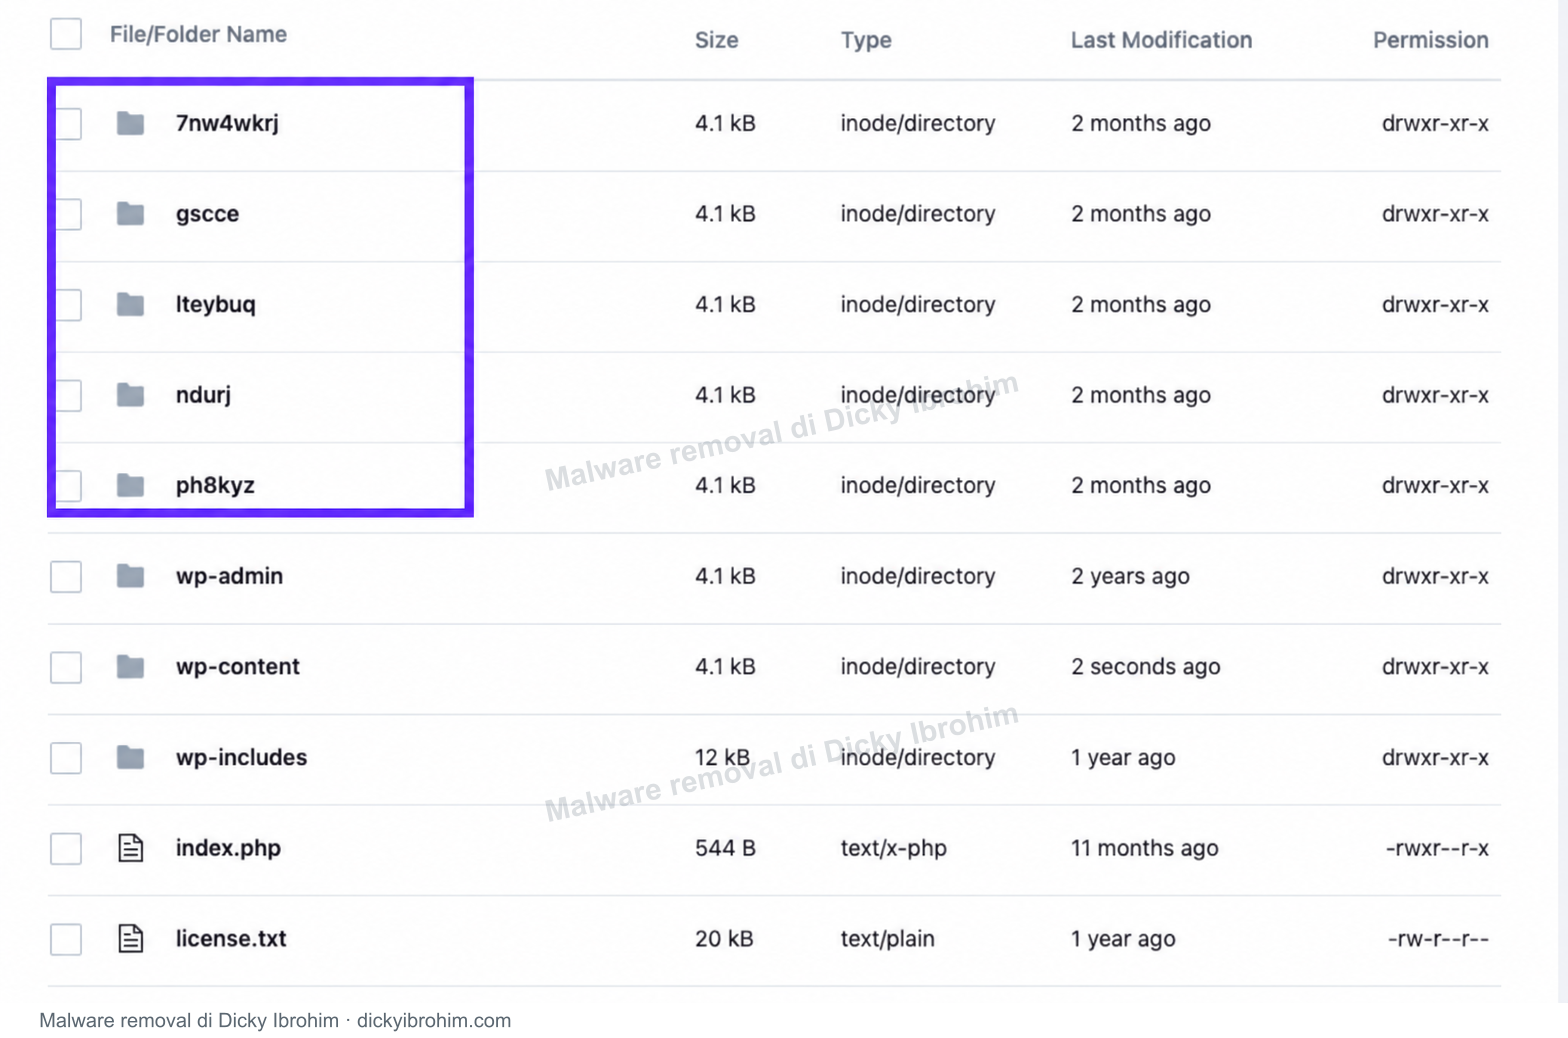 Enlarge documentation
DOCUMENTATION DETAIL
Another view of the highlighted directories. This complements the file inspection; it is not a separate case or outcome.
SYMPTOMS THAT NEED ATTENTION
Deleting one file may leave the source of an infection in place. I follow the symptoms, website structure and available access to determine an appropriate repair.
Tell me what is happeningReproduce the trigger. Trace the unwanted rule. Retest the intended route.
Clean the source and sitemap. Index changes follow the search engine’s process.
An injection can return. Trace its source, address the entry point, then retest.
Clean and retest the destination. Ad decisions remain with the provider’s review.
Inspect the data and available backups before assessing recovery options.
Illustration follows your reading
Redirects may appear only on mobile, from search results, or on particular visits. I inspect the related files, settings and access paths, then retest the conditions that trigger the problem.
Reproduce the trigger. Trace the unwanted rule. Retest the intended route.
Injected pages and unfamiliar sitemaps can fill search results with unwanted content. I remove the spam sources I find, check the sitemap, and help with review steps when Search Console access is available. Search engines control index updates.
Clean the source and sitemap. Index changes follow the search engine’s process.
Changed files, unknown accounts and obfuscated code need to be investigated together. I look for reinfection mechanisms and identifiable entry points, then discuss components that need updating or replacement.
An injection can return. Trace its source, address the entry point, then retest.
I address problems on the destination website and help prepare for a review after cleanup, within the access provided. Approval, review timing and account eligibility remain the advertising provider’s decisions.
Clean and retest the destination. Ad decisions remain with the provider’s review.
I check the condition of the data and available backups before recommending recovery steps. A threatening message alone does not establish that data was encrypted or stolen. Missing data without a usable backup cannot always be recovered.
Inspect the data and available backups before assessing recovery options.
WHAT THE WORK INCLUDES
The work covers one website installation and its related files and database. Handover focuses on remediation results and testing status. Internal technical methods are not included in the handover.
A summary of the website after remediation: issues addressed, retesting results and any remaining limitations.
Cleanup of identified infections within the agreed scope. Additional requirements are discussed before expanding the work or cost.
Reported symptoms and agreed key functions are checked again, so you can assess the website after remediation.
You know the maintenance needs, decisions still required and written warranty terms after the work is complete.
Website
Engineer
Technical
Lead
KNOW WHO TO CONTACT
I am Dicky Ibrohim. I handle the investigation and repairs directly and explain the results and conditions affecting website use. Access limits, data conditions and decisions requiring your approval are made clear. You can decide with an understanding of the scope and cost before work begins.
Your website needs to be useful again. I start with the disruption that is getting in your way.
HOW IT WORKS
Share the URL, when the problem occurs and a screenshot if available. At this stage, describe the issue without sending passwords.
We agree on the scope, handover, timing and cost. Working access is shared through an agreed method after you approve the work.
I record the initial condition and make copies where access permits, then address the infection and related entry points I can identify.
Reported symptoms and related functions are checked again. You receive a results summary, testing status, relevant follow-up requirements and written warranty terms.
PRICED FOR THE SCOPE
Start with the condition of your website. I quote after assessing the work required. Additional installations, licenses and out-of-scope work are discussed separately.
Discuss scope & cost ↗BEFORE WE START
WordPress is included in the service. For another CMS or a custom application, share the technology, symptoms and available access so I can assess whether the work fits my capabilities and service scope.
You receive a summary of remediation results and testing status, including impacts, limitations and follow-up decisions needed from you. This is a hands-on remediation service, not training. Cleanup tutorials, internal scripts or tools and detailed vulnerability information are not part of the standard handover. The handover scope is agreed before work begins.
The service terms give an estimate of 2 to 7 business days after complete access is received. Data volume, hosting conditions, availability of official components and infection complexity can affect timing. Your estimate is discussed before work starts; third-party reviews have their own timelines.
Repeat cleanup for the same incident follows the period agreed in writing. For payment after completion, it starts on the final invoice date after the work is complete; if any cleanup service fee is prepaid, when completion is notified through chat, official WhatsApp, or email. New attacks, later changes, or infection from neighbouring sites are excluded only to the extent they caused the recurrence. Safe replacement access can be coordinated without automatically cancelling a valid claim. The service terms contain the full conditions.
Not always. The outcome depends on damage, usable backups and available official replacement components. I assess recovery options first. Deleted or damaged data without a backup may be unrecoverable, and problematic components may need to be disabled.
Website cleanup and platform decisions are separate processes. I can help with review steps when access is available, but advertising approval, index updates, search positions and timing are determined by each platform.
The website URL, visible symptoms, when the issue began, and hosting or CMS information if known. A pre-incident backup helps. Once the scope is agreed, we determine the access required. Do not send passwords, tokens or customer data through the initial enquiry form.
Cleanup needs ongoing maintenance: updates from official sources, account security, restricted access, tested backups and attention to any other infected installations. Recommendations depend on the findings. No cleanup makes a website immune to every future attack.
START WITH YOUR WEBSITE
Tell me what you have noticed and how it affects your business. I will assess the work required, then discuss the next steps and cost with you.
You do not need to know the malware’s name. A URL and a short description are enough to start.
Do not include passwords, tokens or customer data. Working access will be discussed through an agreed channel.
Your information is only used to respond to this enquiry. Privacy ↗
After receiving your message, we discuss the website, access requirements and estimated cost. You decide whether to proceed.
Prefer to contact me directly?